NIST Project Aims to Accelerate Mobile Driver’s License Adoption
NIST’s new draft report outlines tools and best practices to help organizations adopt mobile driver’s licenses.
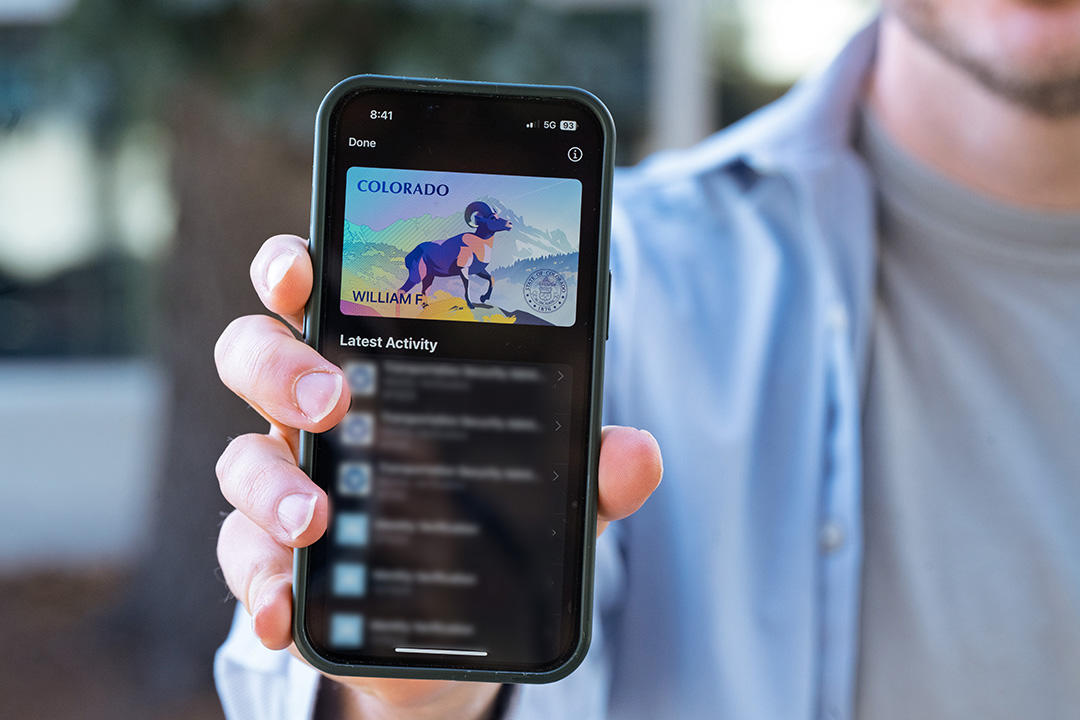
Accelerating Mobile Driver’s License Adoption
Mobile driver’s licenses (mDLs) promise a more secure, convenient way for Americans to prove identity online and in‑person. Yet adoption remains limited because few services accept them. To break this “chicken‑and‑egg” cycle, NIST’s National Cybersecurity Center of Excellence (NCCoE) has released a draft Special Publication (1800‑42) that provides a reference architecture, practical guidance, and best‑practice recommendations for integrating mDLs into existing workflows.
Why mDLs Matter
- Stronger security – Cryptographic protection makes mDLs harder to forge or steal than paper IDs.
- Convenient user experience – No need to upload photos of a physical card; the credential can be presented directly from a smartphone.
- Broad applicability – From opening bank accounts to accessing health records or government benefits, an mDL can serve as a universal digital ID.
The NIST Draft Report’s Core Contributions
- Reference architecture – Demonstrates three key capabilities: presenting an mDL for online identity verification, invoking the mDL in high‑risk scenarios (e.g., large transactions or account recovery), and issuing a phishing‑resistant authenticator (passkey) linked to the mDL.
- Off‑the‑shelf implementation – Built with commercially available hardware, software, and standards, showing that organizations can start today without bespoke solutions.
- Threat model and mitigations – Aligns with existing NIST publications (e.g., Privacy Framework, SP 800‑53 rev. 5) to help adopters manage risks.
- Usability testing insights – Summarizes feedback from volunteer participants, yielding seven best‑practice recommendations to improve the user experience.
Who’s Involved?
The project gathered stakeholders from the mDL ecosystem, including technology firms, government agencies, and five of the ten largest U.S. banks. While the initial demonstration focused on financial services, the guidance is intended for any organization that currently accepts physical IDs and wishes to transition to digital credentials.
Next Steps for the Community
NIST is seeking public comments on the draft report through December 20, 2026. Interested parties can submit feedback via email (mdl‑nccoe@nist.gov) or through the project’s resource hub. Input will help refine the architecture and recommendations before the final publication.
Practical Takeaway
Organizations looking to future‑proof their identity‑verification processes can start by reviewing NIST’s draft report, piloting the reference architecture with existing off‑the‑shelf tools, and contributing feedback to shape the final guidance. Early adoption can position firms ahead of regulatory expectations and improve security for both customers and the broader digital ecosystem.
Source
Read original sourceWhy we picked this
Accepted from curated QuantumUnzipped source (relevance scoring disabled).